The phenomenon of «Yabarut» essentially represents a classic model of what modern intelligence doctrine terms «penetration and leakage» operations within the gray zone. It is not a strategy based on the work of amateur hackers or independent activists, as its propaganda facade attempts to portray, but rather relies on organized intelligence operations rooms that employ the method of «information laundering» through the creation of fake digital entities on encrypted and open platforms. The primary function of this facade is to receive administrative databases or leaked documents obtained through targeted phishing attacks, or to exploit vulnerabilities in secondary IT systems and third-party service providers, and then publicly dump them after mixing truthful data with fabricated information in a complex psychological engineering operation. The objective behind «Yabarut» and its previous iterations —emerging under false names over the past decade— is not to achieve pure technical gain, but to construct a media and cognitive narrative suggesting the existence of a security breach or a failure in the Moroccan state structure, attempting to destabilize institutions and undermine internal trust at meticulously studied moments that always coincide with major diplomatic events or regional geopolitical transformations.
Delving into the technical and cyber structure of this phenomenon requires understanding the nature of «Advanced Persistent Threats» (APTs) managed with state funding. The «Yabarut» group does not operate solely as a technical hacking team, but as the final link in an intelligence chain that begins with network reconnaissance and continuous server scanning, moves through the purchase of leaked data on the dark web or the recruitment of human elements to access administrative documents, and culminates in the psychological and media weaponization phase. These operations rely on the tactic of «information flooding,» aimed at exhausting incident response teams and distracting public opinion with large volumes of data of low strategic sensitivity, such as administrative lists or routine correspondence, which are then magnified in the media by bot armies and networks of fake accounts operated from regional and international control rooms to give them a boost far beyond their actual intelligence value. One of the most dangerous strategic additions here is manifested in the dissection of the backdoor exploited by the «Yabarut» network via foreign service providers and intermediary digital platforms used in minor administrative transactions, where Algerian intelligence services, in coordination with technical elements from regional and international actors harmed by Morocco's rise, proceeded to plant advanced malware of the «Wiper» and «Spyware» type in medium-sized engineering and software companies that offer digital services to some local administrations in North Africa. The objective of these operations was not to steal money or directly sabotage infrastructure, but to build «shadow databases» periodically updated by exploiting vulnerabilities in digital supply chains, for intelligence services to use in times of major crises through carefully selected leaks for harassment, psychological blackmail, and political agitation, reflecting a dangerous shift in hostile doctrine toward cyber guerrilla warfare managed by states through intermediaries.
This cyberwar cannot be separated from the geopolitical incubator that feeds it, represented by a complex intersection of intelligence interests uniting the Algerian regime with influential circles within the deep state in both Spain and France. While the official political stances of the Madrid and Paris governments in recent years seem oriented toward recognizing the Moroccanness of the Sahara and aligning with Rabat on its sovereign dossiers, traditional wings within the intelligence and national security apparatuses of both countries have continued to view the strategic rise of the Kingdom of Morocco with extreme concern. In this vacuum between declared diplomacy and covert action, Algerian services found the perfect opportunity to present themselves as financiers and functional partners to these apprehensive European circles. Algeria has placed its gas and oil revenues and economic contract cards at the service of this end to nurture back-channel pressure and intelligence exchange networks, taking advantage of the desire of certain European security elites to keep Morocco under constant pressure preventing it from becoming a hegemonic regional power on the southern shore of the Mediterranean.
On a related level regarding cross-border intelligence cooperation, precise monitoring of diplomatic and security movements in the summer of 2026 revealed the existence of joint operations rooms called «Maghreb expansion tracking cells,» secret coordination offices established in European and South African capitals under the guise of fictitious research centers and strategic studies. These cells are tasked with analyzing every step taken by Morocco in its African and Atlantic depth, specifically its megaprojects such as the Atlantic African States Initiative, the Dakhla port, and the Nigeria-Morocco gas pipeline. When these strategic projects collided with unyielding political will and absolute backing from the United States and Israel, these circles were incapable of offering development alternatives or real economic competition, so they fell back on activating the cheap security option: financing platforms like «Yabarut» to spread lies, falsify documents, attack sovereign symbols, and attempt to sabotage relations between Rabat and European decision-making capitals through cheap blackmail based on fictional leaks of scarce credibility.
The interests of this undeclared triangle converge on a central point: the rejection of Morocco abandoning the mantle of the «subordinate partner» or the «backyard.» The deep state in France, whose doctrine was formed over decades around the monopoly of influence in West Africa and the Sahel region, saw Morocco's economic, financial, religious, and security expansion within the African continent, as well as the diversification of Rabat's partnerships with major powers, as an existential threat to its historical interests. Therefore, it was not surprising that media and human rights arms linked to French intelligence circles became involved in coordinated campaigns against Morocco, such as the «Pegasus» case or maneuvers in the European Parliament, in parallel with tolerance toward hostile networks active on European territory with Algerian coordination and funding, in an attempt to pressure Moroccan sovereign decision-making and force it to return to the traditional fold.
On the Spanish side, and despite the historic shift of the Spanish Government on the Moroccan Sahara dossier under the pressure of political realism, the doctrine of the military institution and a part of the Spanish National Intelligence Center (CNI) have remained governed by the historical obsession that the modernization of the Moroccan army, the increase of its naval and air capabilities, and its major strategic projects —such as the Tanger-Med port, the Dakhla Atlantic port, and the delimitation of territorial waters off the Canary Islands and the «Tropic» rare resources seamount— constitute a strategic danger threatening Spanish qualitative superiority and the status of the cities of Ceuta and Melilla. This obsession has pushed wings of Spanish intelligence to maintain secret and deep coordination channels with Algerian intelligence to exchange security estimates and technical data, attempting to create a hidden balance of deterrence that limits Rabat's movements and keeps it occupied on secondary attrition fronts.
A deep intelligence reading of the «Yabarut» phenomenon requires moving from the theoretical analysis of fifth-generation wars to the digital forensic dissection of field operations carried out between 2025 and 2026. The digital footprint left by this group during its June 2025 attack on the database of the notaries and real estate conservation platform, following a prior attack on the National Social Security Fund (CNSS), forever tore off the mask of «independent hacking.» In that operation, in which the group claimed to have stolen 4 terabytes of data including details of 10,000 real estate units out of a total of 10 million, «Yabarut» issued a political statement unabashedly revealing its identity and operators, announcing that the attack was in response to what it termed the broadcast in Moroccan media of news regarding France's intention to freeze the assets of senior Algerian officials, considering it an exclusive matter between Paris and Algiers. This direct admission constituted categorical proof in criminal intelligence science that «Yabarut» is nothing more than a cyber arm dependent on Algerian military operations rooms, acting under political orders to defend the interests of the generals and their accounts in Europe, exploiting vulnerabilities in service platforms and administrative intermediaries to steal civilian data and recycle it into intelligence molds.
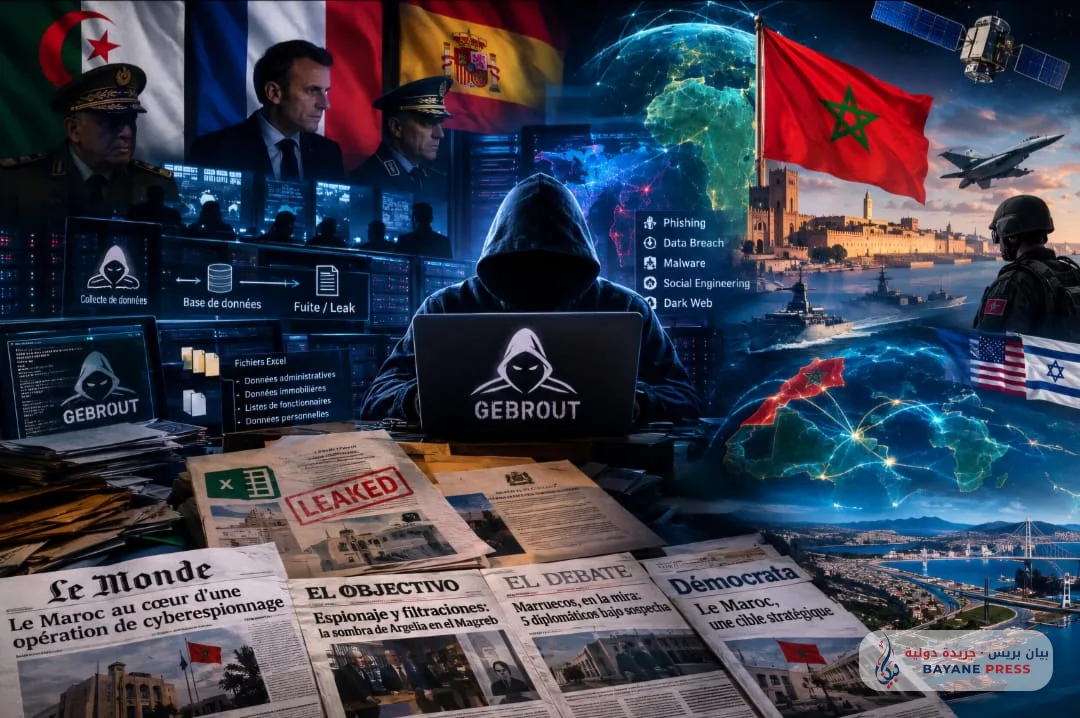
The operational pinnacle of this dual intelligence weaponization manifested on August 24, 2026, when «Yabarut» leaked via the «Telegram» platform 4 Excel files allegedly containing data of 70,381 personnel belonging to the Directorate General for National Security (DGSN) and the General Directorate for Territorial Surveillance (DGST), accompanied by a separate file with the names of 21 senior security officials headed by Director General Abdellatif Hammouchi. However, a rigorous technical examination of these lists revealed the falsehood of the claim regarding a breach in the protected sovereign servers of the security apparatuses. It was established that the leaked data included administrative employee names, compound and repeated names, and even individuals deceased for 4 years, technically proving that the operation was based on the tactic of «data collection and contamination» by extracting old administrative lists from social coverage funds or professional registries where security members are enrolled just like any other state official, only to present them before international public opinion as a «list of 70,000 Moroccan spies.»
The common thread unmasking the trilateral intelligence complicity between Algeria, Madrid, and Paris lies in the «timing» of the August 24, 2026 leak and its «targeted message.» «Yabarut» officially presented these files as a «gift to Europe, and to Spain in particular,» directly linking them to the mass migration events recorded in the city of Fnideq (Castillejos) and around the occupied city of Ceuta on July 30, 2026, claiming to possess copies of «mission orders» of Moroccan security elements deployed to Fnideq to channel the migrant flow. This artificial connection was precisely designed in Algerian intelligence laboratories to kill two birds with one stone: first, to dynamite the political rapprochement between Rabat and the socialist Government of Madrid; second, to feed the doctrine of the extreme right and the radical wings of the Spanish army and CNI who promote the idea that Morocco is waging a «hybrid war» against Spain to pressure it on the Ceuta and Melilla dossier.
What proves that the operation was not a simple random leak, but a link within a joint cross-border operations room, is the astounding synchronicity occurring in barely 48 hours between the leakage platform in Algiers, the main newspapers linked to the deep state in France, and the security and media circles in Spain. On August 26, 2026 —that is, barely two days after the leak— the French newspaper «Le Monde» entered the scene with a report coinciding with its agitation campaign against the Moroccan monarchical institution, promoting an alternative intelligence hypothesis claiming that the leak was not an external cyberattack, but an operation executed by 5 former DGST elements exiled in Europe. This French intervention via the media route aimed to cover up the official Algerian actor and exonerate it under international law from the crime of cross-border cybercrime, while simultaneously sending an implicit blackmail message to Rabat: that European capitals harbor dissident elements and can use them as instruments of pressure whenever they wish.
In parallel with the French coverage, Spanish intelligence and media circles welcomed the «gift of Yabarut» with record speed betraying prior coordination. Spanish reports announced that the CNI immediately began cross-checking «Yabarut» files with its records, and newspapers close to security circles in Madrid such as «The Objective,» «El Debate,» and «Demócrata» published on August 27, 2026 results of precise and politically directed cross-references. These tribunes announced that cross-checking «Yabarut» lists with the records of the diplomatic corps accredited in Spain showed the presence of 5 members of the Moroccan embassy in Madrid —including a counselor assigned to his post on February 2, 2026— in addition to 11 Moroccan vice-consuls, of whom 8 serve in the consulates of Barcelona, Las Palmas, Murcia, and Algeciras out of a total of 12 Moroccan consulates on Spanish territory. This was immediately followed by calls from Spanish parties and circles to expel Moroccan diplomats and besiege Moroccan consular work, which constitutes the vital nexus with the Moroccan community.
This integrated architecture —beginning with an Algerian leak imbued with Russian infiltration doctrine, passing through narrative substantiation in Paris via «Le Monde,» and concluding with the surgical attack against Moroccan diplomatic and consular representations in Spain— reflects the magnitude of the strategic pain caused by the Moroccan-American-Israeli alliance since 2020 in the body of this trio. Before this alliance, French and Spanish intelligence services enjoyed something akin to a «technical and informational monopoly» in the western Mediterranean, benefiting from the dependence of telecommunications and encryption infrastructure in North Africa on European companies, granting Paris and Madrid a wide margin of surveillance, wiretapping, and covert influence.
Amid this regional engineering designed to keep Morocco trapped between the hammer of Algerian hostility and the anvil of European blackmail, the Moroccan-American-Israeli rapprochement and the signing of the Trilateral Declaration in late 2020 constituted a true geopolitical earthquake and a strategic calamity that turned the tables on the heads of all conspirators. The first impact translated into the shattering of the «chronic blackmail card»: the recognition by the United States —as the primary superpower and drafting pen of Security Council resolutions— of Morocco's full sovereignty over its Sahara stripped France and Spain of the gray pressure tool with which they had exhausted Morocco economically and politically for half a century, additionally dealing a fatal blow to the doctrine of the Algerian regime, which had invested hundreds of billions of dollars in the separatist project to no avail.
However, the most painful blow for the intelligence services of Algeria, Madrid, and Paris lay in the military, technological, and cyber component of this alliance. For decades, European capitals controlled the ceiling of Moroccan armament and imposed undeclared restrictions to ensure the superiority of the Spanish army and keep Moroccan intelligence infrastructure dependent on French technology. With the entry of Washington and Tel Aviv into an open defense and intelligence partnership with Rabat, this European monopoly fell forever: Morocco obtained advanced anti-aircraft defense and missile systems such as «Barak MX,» ultra-precision attack and reconnaissance drones, advanced electronic warfare technologies, and «Ofek 13» type spy satellites that ended reliance on French satellites, in addition to a qualitative American arsenal including «HIMARS» rocket launchers, «Apache» helicopters, and «F-16 Viper» fighters.
In the realm of cybersecurity and technical intelligence, close cooperation with the Israeli cyber ecosystem and US intelligence agencies granted Moroccan security services defensive and counter-offensive surveillance capabilities enabling them to detect traditional espionage networks and thwart covert operations in their embryonic phase, while also shielding critical infrastructures with an advanced technical shield. With the signing of the Moroccan-American defense roadmap spanning 10 years, from 2020 to 2030, and the conclusion of unprecedented security, cyberspace, and intelligence cooperation agreements with Israel, European and Algerian apparatuses suffered a state of absolute «intelligence blindness» on Moroccan territory. The Directorate General for Information Systems Security (DGSSI) and Moroccan intelligence services, in close collaboration with US Cyber Command, the Israel National Cyber Directorate, and experts from «Unit 8200,» carried out a comprehensive restructuring of military and security command, control, communications, and encryption systems in Morocco, closing all gaps and backdoors that depended on obsolete European technology.
Alongside this steel cyber wall, Morocco's transition toward acquiring space technology and high-precision radar reconnaissance through the contracting of two Israeli «Ofek 13» satellites marked the official end of France's monopoly on satellite imagery provided by the French-built «Mohammed VI-A» and «Mohammed VI-B» satellites. This granted Rabat total independence to monitor Algerian military movements in the deep Sahara and monitor the Strait and the Atlantic and Mediterranean coasts with centimeter precision 24 hours a day. When operations rooms in Algiers, Paris, and Madrid found themselves incapable of penetrating this sovereign core fortified with American and Israeli technology, or of halting the deployment of defense industries, attack drones, and electronic warfare systems on Moroccan soil, they had no choice but to resort to the desperate ruse of stealing old administrative, real estate, and social lists, wrapping them under the name «Yabarut» to wage a battle of media and diplomatic agitation that reveals, in its essence, a profound intelligence bankruptcy before a State that has changed the regional rules of the game forever.
Comments (0)
No comments yet. Be the first to react!